Fixed-scope assessments, independent validation, embedded senior advisors and board education — all delivered through the CyberPrism platform, so every finding is evidenced, every roadmap is live, and every report is written for the boardroom.
Fixed-scope, evidence-based assessments that establish your true position against the regulation that matters to you — each one delivered on CyberPrism and closed with a board-ready report.
A structured gap analysis across DORA's pillars — ICT risk management, incident reporting, resilience testing, third-party risk and oversight — closed with a prioritised remediation roadmap.
Starts with the question most organisations can't yet answer: are you in scope — and as an essential or important entity? Then a gap analysis against your NIS2 obligations, with management accountability front and centre.
Role and risk classification for your AI systems, and a governance gap analysis mapped to the EU AI Act, NIST AI RMF and ISO/IEC 42001 — with a proportionate plan to close what matters.
Not sure which of these applies to you, or where you'd score? Get an instant, theme-by-theme readiness score across DORA, NIS2 or the EU AI Act — no cost, no obligation.
Your resilience is only as strong as your critical providers. A structured review of your supplier estate — register of information, criticality tiering, and oversight gaps against DORA and NIS2 third-party obligations.
High-impact briefings that turn threat trends and regulatory change into clear board decisions — plus certified executive programmes through our exclusive ICTTF / EU Cyber Academy partnership.
Reported maturity and operational reality are rarely the same thing. Our flagship engagement closes that gap.
When the assessment is done and the roadmap is agreed, most organisations need one more thing: senior ownership to make it happen.

Independent advisors at your board's side before, during and after an incident — so the worst week of your year is governed, evidenced and defensible. We govern the response and the reporting; your technical responders handle the forensics.
A named senior owner for your digital resilience: board-ready oversight, structured challenge, and a credible regulatory interface — without the cost or delay of a full-time hire.
Resilience run as a continuous programme, not a one-off project: a monthly session with your dedicated senior advisor, a live roadmap maintained in CyberPrism, and a quarterly board update.
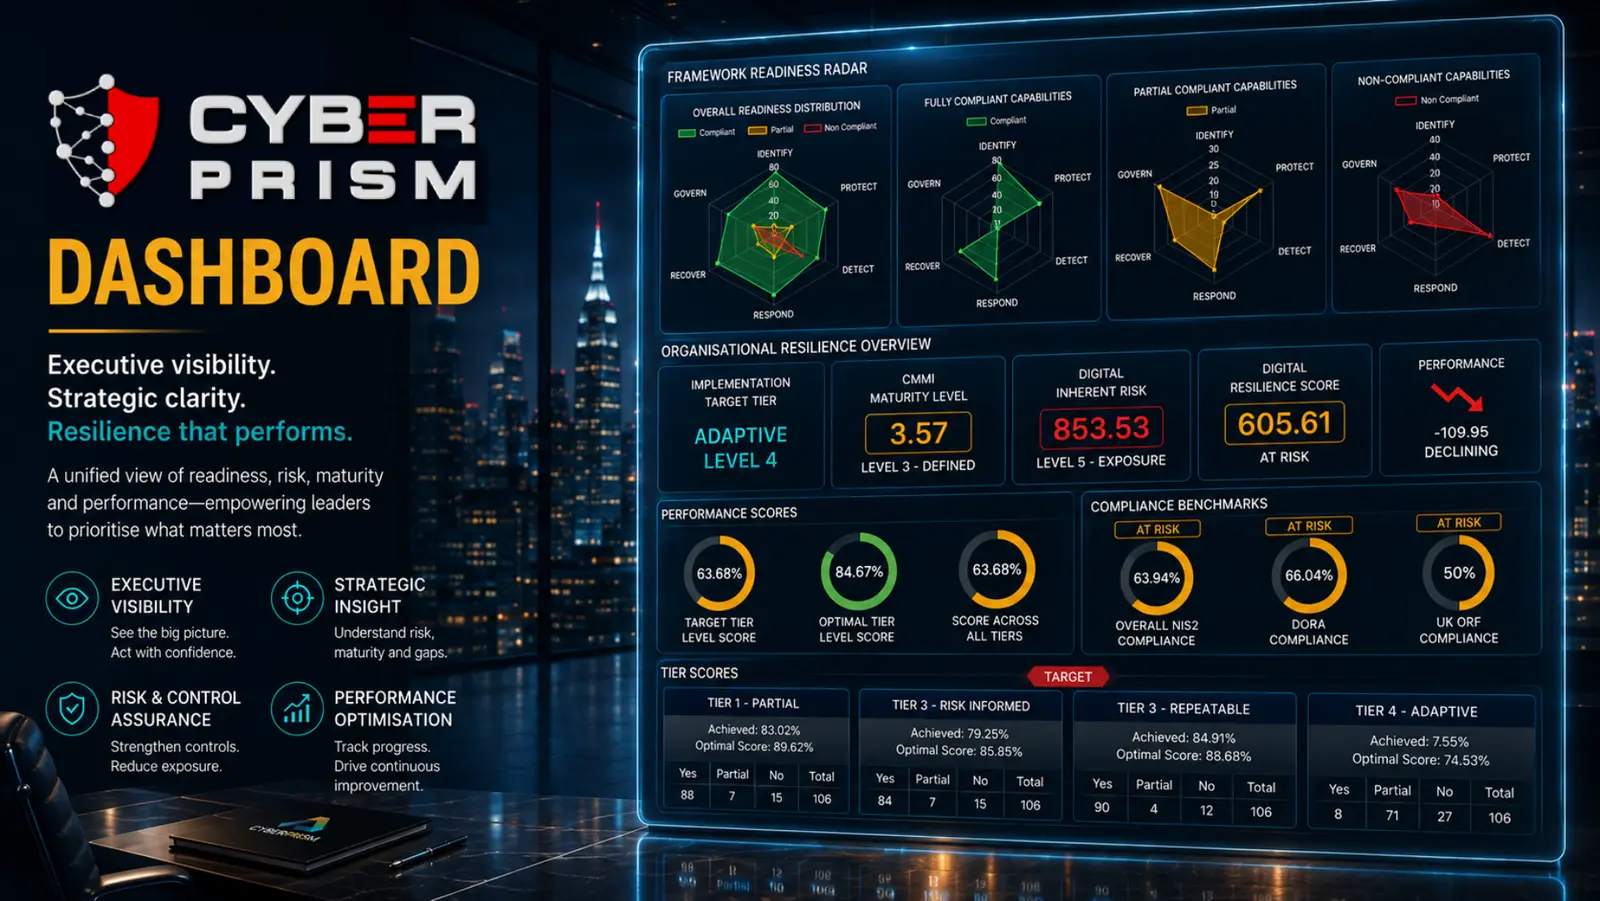
Every CRI engagement runs on CyberPrism, our digital resilience platform — assess once, and see your posture through the lens of each framework that applies to you, with every finding evidenced and every change tracked.
Structured, proportionate pathways designed around the supervisory reality of specific sectors.
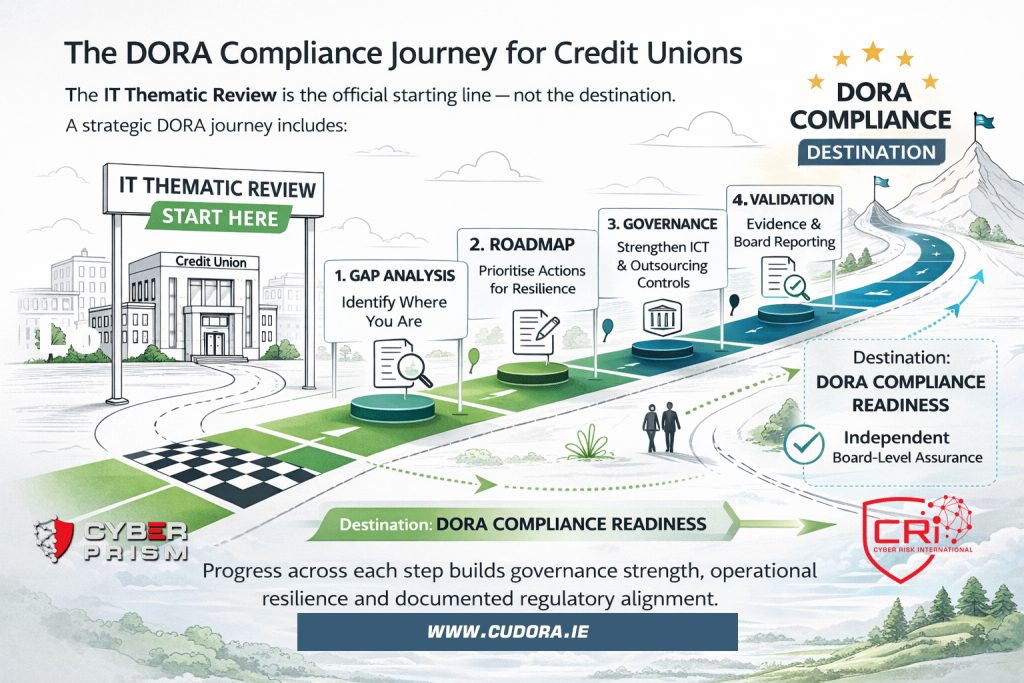
The managed pathway from the Central Bank's IT Thematic Review to DORA compliance readiness — built specifically for Irish credit unions, with optional independent board-level sign-off.
Explore CUDORA →
Digital resilience for the guardians of digital trust — case studies, board education and resilience programmes for hospitals and health organisations across Europe.
Explore health sector resilience →Every engagement starts with a short, no-obligation scoping conversation — or call us on +353 (0)1 905 3260.