Leadership Profile · Cyber Risk International

Paul C Dwyer

Global cybersecurity, risk & compliance authority
CEOCISOAuthorBoard AdvisorPublic SpeakerPodcast HostEntrepreneur
30+ yearsacross military, law enforcement & commercial sectors
30,000+professionals in the ICTTF community he founded
Top 100Ireland's CEOs — Business & Finance
Paul C Dwyer speaking on stage
Founder & President of the ICTTF · CEO of Cyber Risk International

Profile

Paul C Dwyer stands among the world's leading cybersecurity, risk and compliance authorities. As CEO of Cyber Risk International, he excels in corporate and enterprise security, crafting cyber defence programmes and safeguarding business operations for clients. He is also the founder and President of the ICTTF International Cyber Threat Task Force, leading a community of over 30,000 professionals in their mission to combat cyber threats and promote industry diversity.

With more than 30 years of experience across military, law enforcement and commercial sectors globally, Paul has served as an advisor to governments and intelligence agencies, and as Interim Global CISO for multiple multinational organisations. A renowned international speaker and host of the "Cyber Task Force" podcast, he is a sought-after media contributor and thought leader — and the author of The Art of Cyber Risk Oversight and Cyber Risk Leadership.

Track record

Leadership roles, accreditations and affiliations spanning three decades at the front line of cyber risk.

Leadership roles

  • President — ICTTF International Cyber Threat Task Force
  • Co-Chairman — UK National Crime Agency Industry Group
  • Advisor to NATO — Countering Hybrid Cyber Threats
  • Interim Global CISO — multiple multinational organisations

Certifications & approvals

  • ISC2 — International Information System Security Certification Consortium
  • ISACA — Information Systems Audit and Control Association
  • National Crime Faculty — approved
  • HTCN — High Tech Crime Network, approved

Fellowships & memberships

  • Fellow — Irish Computer Society
  • Member — Institute of Directors (IoD), IIEA, Institute of Risk Management (IRM)
  • Diploma in Corporate Governance — Corporate Governance Institute
  • Harvard certification — Higher Education specialist
Ethical hackingDigital forensicsRisk managementBusiness continuityInternational governance frameworksFinancial services regulationCyber lawProject management

Watch Paul in action

Keynotes, briefings and interviews on cyber risk, leadership and regulation.
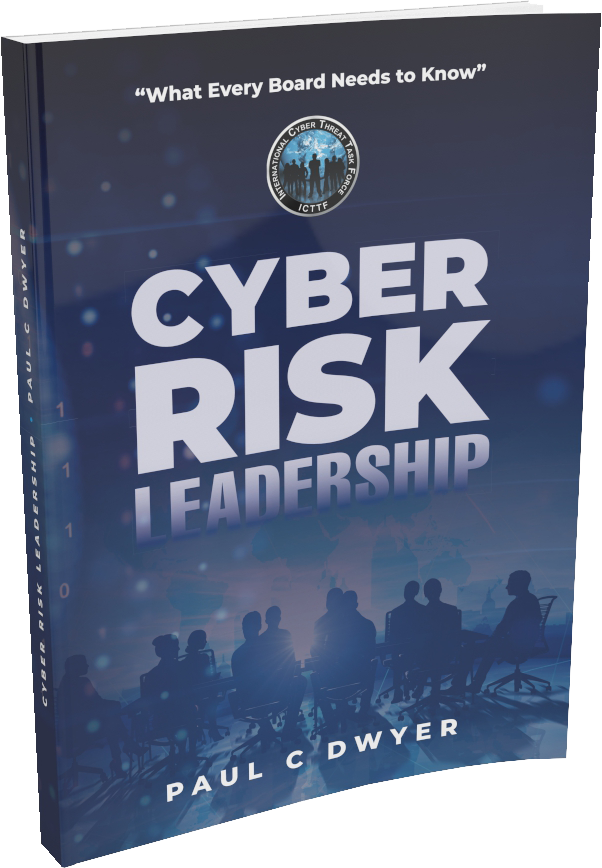
Cyber Risk Leadership book cover by Paul C Dwyer

Cyber Risk Leadership

By Paul C Dwyer · also author of The Art of Cyber Risk Oversight
"What every board needs to know — an executive briefing developed specifically for the business leaders of the financial sector."

A non-technical, business-focused briefing giving leadership clarity on the global cyber risk landscape: the objectives of threat actors, the interplay of geopolitics and cybercrime, the growing burden of regulation, and the anatomy of an attack.

It concludes with the role of leadership in meeting the cyber challenge — aligning cyber strategy with business strategy, meaningful metrics, G7 guidance, and ten key actions for assuring your organisation's cyber resilience status.

Bring this expertise
into your boardroom.

Keynotes, executive briefings, board advisory — talk to us about working with Paul and the CRI team.
strategic leadership

Digital Resilience with CRI

Cyber Risk International empowers organisations to achieve true digital resilience through expert-led advisory, integrated technology, and executive education — enabling leadership to confidently navigate complex threats and regulatory demands.

Cyber Risk International Ltd
Unit 8 Kinsealy Business Park, Kinsealy Lane, Co Dublin, K36 CX92, Ireland
Registered Company: 550801 VAT: IE 329285TH DUNS: 985605977

W: www.cri.ie E: [email protected] P: +353-(0)1-905 3260